
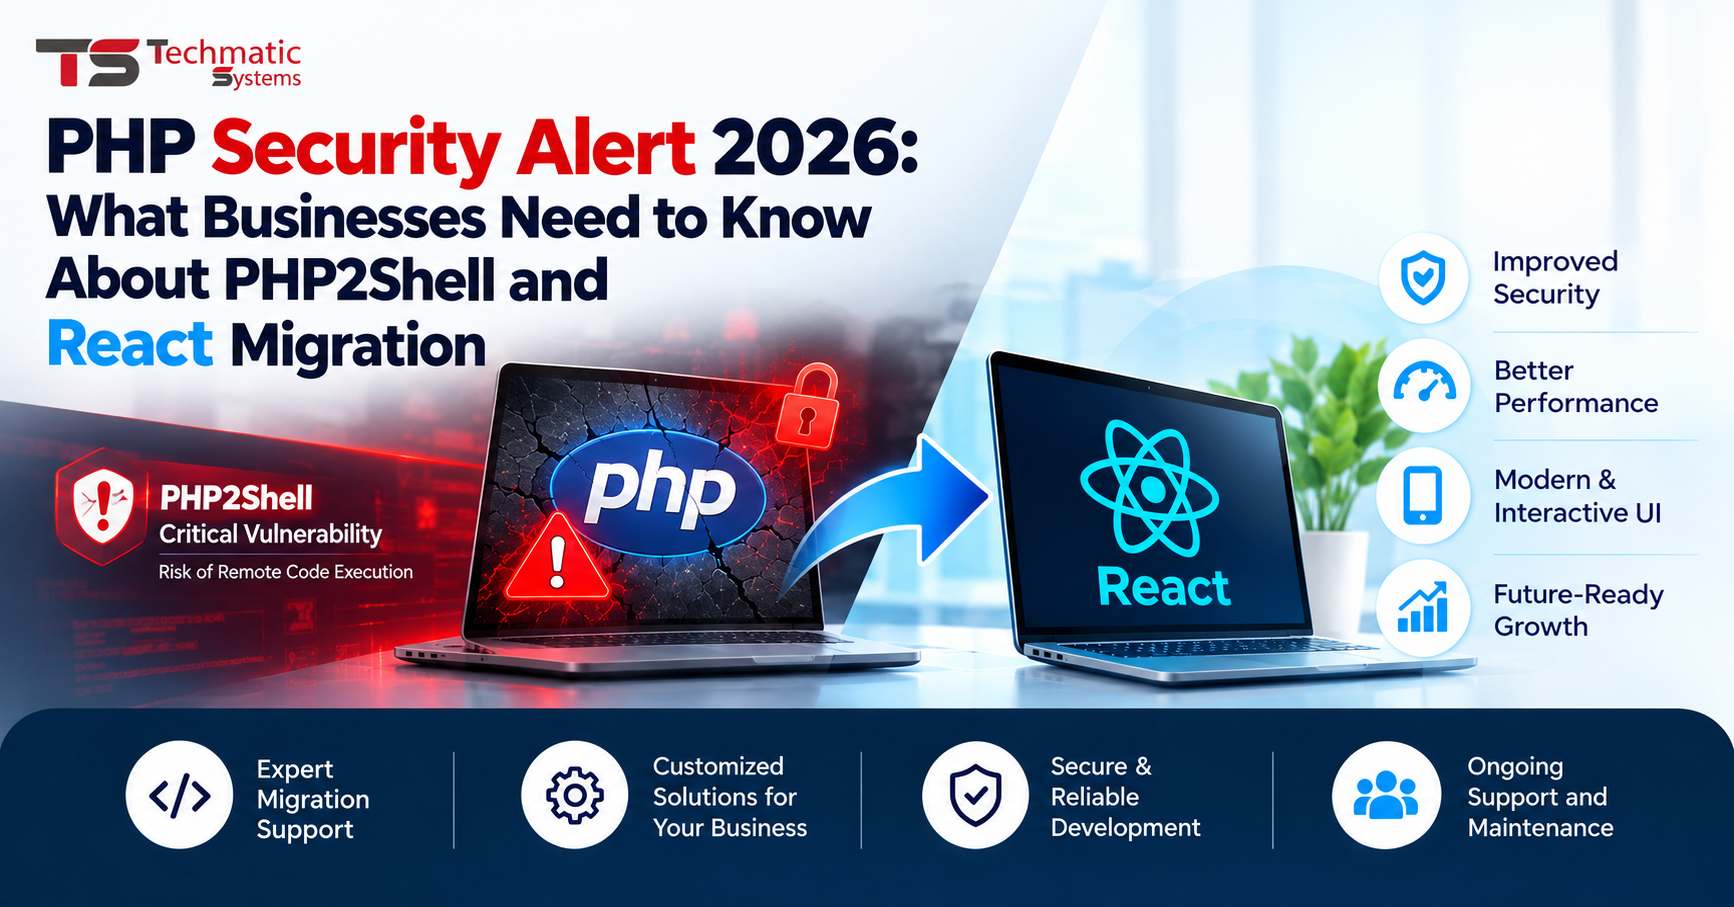
Is your website protected against the latest PHP security vulnerabilities? A recent security alert has put PHP-based applications under renewed scrutiny, highlighting the importance of timely security updates, supported software versions, and a well-maintained application architecture.
On October 21, 2026, the PHP development team released security updates addressing two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619. These flaws can allow unauthenticated remote code execution in affected environments, potentially putting application servers and the data they process at risk.
The vulnerabilities have been discussed under the name PHP2Shell. Security guidance from PHP and major cybersecurity organizations urges businesses to identify affected systems and apply the appropriate updates.
For businesses operating PHP-based websites and applications, the priority is clear: address the immediate security risk, review the existing technology stack, and determine whether the application is ready to support future business requirements.
At Techmatic Systems, we believe this is also an opportunity to have a practical conversation about application modernization, including whether a React-based frontend could benefit your business.
What Is the PHP2Shell Security Alert?
PHP is a widely used server-side programming language that powers websites, content management systems, and business applications. Like any software runtime, PHP requires ongoing maintenance and security updates to address newly discovered vulnerabilities.
The October 2026 PHP security alert concerns two critical vulnerabilities in the PHP runtime. According to published technical guidance, both have a CVSS severity score of 9.2 out of 10.
The vulnerabilities are:
- CVE-2026-109618: A flaw associated with PHP’s handling of out-of-memory conditions and partially initialized request data.
- CVE-2026-109619: A flaw involving internal request state that can remain accessible after its underlying memory has been released.
Under certain conditions, these weaknesses can allow an unauthenticated attacker to execute malicious code on a vulnerable server.
The potential consequences include unauthorized access, server compromise, disruption of business operations, and exposure of sensitive information. Actual impact depends on the affected environment and whether exploitation succeeds.
The PHP development team has released security updates for supported branches. Businesses should consult the official PHP advisory to confirm the applicable version and remediation steps.
Official references:
- PHP security advisory: https://www.php.net/archive/2026.php
- Google Cloud technical guidance: https://cloud.google.com/blog/products/identity-security/responding-to-core-php-vulnerabilities-cve-2026-109618-cve-2026-109619
Which PHP Versions Are Affected?
Published technical guidance identifies PHP versions from 5.4 through 8.5.11 as affected by these vulnerabilities. The PHP team has released fixes for supported branches in the following versions:
| PHP branch | Fixed version |
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
These versions reflect the security release announced on October 21, 2026. Check the official advisory for any subsequent updates before making changes.
PHP 8.1 and earlier are no longer supported by the PHP project for these fixes. Businesses running unsupported versions should prioritize a supported upgrade path rather than assume that a security patch will be available.
Remember that checking the version installed on a developer’s computer is not enough. The production server, hosting environment, container images, and deployment pipeline must also be reviewed.
What Should Businesses Do After the PHP Security Alert?
Before making a major technology change, businesses should address the immediate vulnerability and establish the current state of their application.
1. Identify Your PHP Version
Ask your development team or hosting provider to confirm which PHP version is running in production. Check all relevant environments, including staging servers, containers, and secondary applications.
Some commercial products and hosting solutions include PHP components even when businesses do not directly manage the PHP runtime.
2. Apply the Appropriate Security Updates
Upgrade affected installations to the applicable patched version and redeploy where required. Test the application after updating to identify compatibility issues.
If immediate remediation is not possible, follow official security guidance on restricting exposure while a fix is prepared.
3. Review Dependencies and Server Configuration
Outdated libraries, insecure configuration, weak access controls, and neglected maintenance can create additional risks beyond the current PHP vulnerabilities.
Review dependencies, authentication and authorization, API access, server permissions, and deployment practices as part of a broader security assessment.
4. Check for Signs of Compromise
Patching closes the identified vulnerability, but it does not establish whether a system was previously compromised.
Where exposure or suspicious activity is suspected, review relevant application and server logs, investigate unusual processes or file changes, and follow an appropriate incident-response process.
5. Plan for Long-Term Maintenance
Security is an ongoing responsibility. Establish a process for monitoring updates, maintaining supported software versions, testing changes, and reviewing application security regularly.
These actions help businesses address the immediate issue without overlooking the longer-term health of their technology infrastructure.
Should You Migrate from PHP to React?
The recent PHP security alert has prompted businesses to reconsider their existing technology stacks. However, it is important to understand the difference between fixing a vulnerability and modernizing an application.
React is a JavaScript library for building user interfaces. It is not a direct replacement for PHP’s server-side capabilities.
PHP can continue handling backend logic, database interactions, and server-side processing while React powers a modern frontend. Alternatively, a business may choose a broader architectural change if its requirements justify it.
A React migration may be worth considering when an existing application is difficult to maintain, has a limited user experience, or requires a more flexible frontend to support future features.
When React Migration May Make Sense
- You need a more interactive user experience
React supports component-based interfaces for interactive dashboards, customer portals, account management tools, and other applications that need responsive user interactions.
- Your frontend has become difficult to maintain
Reusable components and clearer interface boundaries can help teams manage complex user interfaces and develop new features more consistently.
- Your business needs to evolve faster
A well-planned frontend architecture can make it easier to introduce new features, improve existing workflows, and support changing business requirements.
- Your application needs a broader modernization plan
If your current application has tightly coupled components, outdated dependencies, or growing maintenance challenges, a modernization project can evaluate which parts should be retained, improved, or replaced.
- You want a technology strategy aligned with future growth
Modernization can create opportunities to improve integration capabilities, maintainability, and the overall development process. The results depend on the architecture, implementation quality, and ongoing maintenance.
Does React Make Your Website More Secure?
React does not automatically make a website more secure than PHP.
The PHP2Shell vulnerabilities affect the PHP runtime. Introducing React on the frontend does not remove a vulnerable PHP backend or fix its dependencies.
A secure modernization project should therefore address both immediate remediation and the application’s wider security controls. These may include supported runtime versions, secure APIs, authentication, authorization, input validation, dependency management, and infrastructure configuration.
The right goal is not simply to replace one technology with another. It is to build and maintain an application that meets your business needs while following sound security practices.
PHP vs. React: Understanding the Difference
PHP and React serve different purposes, so they should not be treated as interchangeable technologies.
| Area | PHP | React |
| Primary role | Server-side application development | Frontend user interfaces |
| Common use | Backend logic, server-rendered pages, data processing | Interactive pages, dashboards, reusable UI components |
| Data handling | Can communicate with databases and process server-side data | Commonly consumes data from APIs |
| Security responsibility | Secure runtime, backend code, dependencies, and configuration | Secure interface implementation and safe integration with the backend |
| Modernization role | Can be upgraded, refactored, or retained | Can modernize the frontend while PHP remains the backend |
For many businesses, the practical option is to retain a suitable PHP backend and introduce React where it adds value. Other applications may benefit from a larger redesign.
The decision should be based on the existing architecture, business goals, technical debt, security requirements, available budget, and future roadmap.
How to Plan a Successful PHP to React Migration
A migration should begin with an assessment, not an immediate rewrite. A structured approach helps reduce unnecessary development work and supports a more predictable transition.
Step 1: Assess the Existing Application
Review the current PHP version, dependencies, server configuration, database structure, APIs, integrations, and user-facing functionality. Document the issues that need to be addressed.
Step 2: Resolve Immediate Security Risks
Apply the appropriate PHP security updates and investigate any suspected compromise before treating the migration as the solution.
Security remediation should not be postponed until a frontend redevelopment project is complete.
Step 3: Define the Migration Scope
Identify the frontend components that would benefit from React. Determine which backend services can remain in PHP and whether any server-side changes are necessary.
A phased migration may be more practical than rebuilding the entire application at once.
Step 4: Plan APIs and Data Flows
Define how the React frontend will communicate with the backend. Review API permissions, authentication, data validation, error handling, and performance requirements.
Step 5: Test Before Launch
Test critical business workflows, integrations, responsive layouts, accessibility, performance, and security controls. Establish a rollback plan before deployment.
For public-facing websites, preserve important URLs wherever possible. If URLs change, implement appropriate redirects and review metadata, canonical tags, internal links, and XML sitemaps.
Step 6: Monitor and Improve
After launch, monitor application errors, performance, security updates, and user feedback. Continue maintaining both frontend and backend components.
A successful migration is not just a new interface. It is a maintainable solution that supports business requirements over time.
How Techmatic Systems Can Help
At Techmatic Systems, we understand that every application has different technical requirements and business priorities. A major security alert can raise important questions about whether your existing website is secure, maintainable, and ready for future growth.
Our team can help you assess your current PHP application, identify modernization opportunities, and determine whether a React-based frontend or a broader technology upgrade is appropriate.
Depending on your requirements, the work may include:
- Application assessment: Review the existing architecture, dependencies, technical limitations, and business requirements.
- React frontend development: Build modern, responsive interfaces with reusable components where appropriate.
- Backend modernization: Improve the existing PHP backend, integrations, and application structure where needed.
- Migration planning: Define the scope, testing approach, deployment strategy, and steps needed to minimize disruption.
- Ongoing maintenance: Support updates, performance improvements, and continuous application improvements.
Our approach is collaborative. Rather than recommending a complete rebuild by default, we focus on identifying the changes that provide meaningful value for your business.
If your application is becoming harder to maintain, limiting new features, or creating concerns about future scalability, our team can help you evaluate the available options and plan the next steps.
The October 2026 PHP security alert is a reminder that application security requires continuous attention. Businesses should begin by identifying affected PHP installations, applying the appropriate fixes, and investigating any signs of compromise.
For organizations facing growing maintenance challenges or planning new digital capabilities, this is also a useful time to evaluate the long-term direction of their applications.
You do not have to navigate that decision alone.
Techmatic Systems can help you assess your current application, explore React migration options, and plan a practical path toward a modern, maintainable, and future-ready digital solution.
Ready to review your application?
Contact Techmatic Systems to discuss your requirements and explore the right modernization strategy for your business.
Frequently Asked Questions
1. What is the PHP2Shell vulnerability?
PHP2Shell refers to two critical PHP runtime vulnerabilities, CVE-2026-109618 and CVE-2026-109619, disclosed in October 2026. Under affected conditions, they can allow unauthenticated remote code execution. Businesses should check the official advisory and apply the appropriate security updates.
2. Is migrating from PHP to React necessary after the security alert?
No. The immediate priority is to patch affected PHP installations and investigate potential exposure. React migration is a separate architectural decision that may be useful when the frontend needs modernization.
3. Can React replace PHP completely?
React primarily builds user interfaces and does not provide all the server-side capabilities of PHP. A React application can use a PHP backend through APIs. Replacing the backend requires a separate technology and architecture decision.
4. Which PHP versions have security fixes for the October 2026 alert?
The announced fixed versions are PHP 8.2.35, 8.3.36, 8.4.27, and 8.5.12. Verify the latest official PHP advisory before upgrading, as subsequent security releases may change the recommended versions.
5. Will React migration improve Google rankings?
React does not guarantee better search rankings. Search visibility depends on factors such as useful content, crawlability, rendering, page experience, technical SEO, and overall site quality. A migration should preserve important URLs and metadata and be tested to ensure search engines can access the intended content.
6. How can Techmatic Systems help with PHP application modernization?
Techmatic Systems can assess your existing application, identify technical and security priorities, plan a suitable migration, develop a React frontend where appropriate, and support ongoing maintenance. The recommended scope depends on your current architecture and business goals.